

随着 Android 转向持续发布和季度公告(作为基于风险的安全更新的一部分),OEM 可能希望在发布版本之间修复漏洞,而不是等待整个季度。借助补充安全补丁 XML 功能,OEM 可以通过提供标准化的 XML 文件来报告已修补的 CVE(超出声明的安全补丁级别 [SPL]),从而获得持续修补的认可。
概要流程
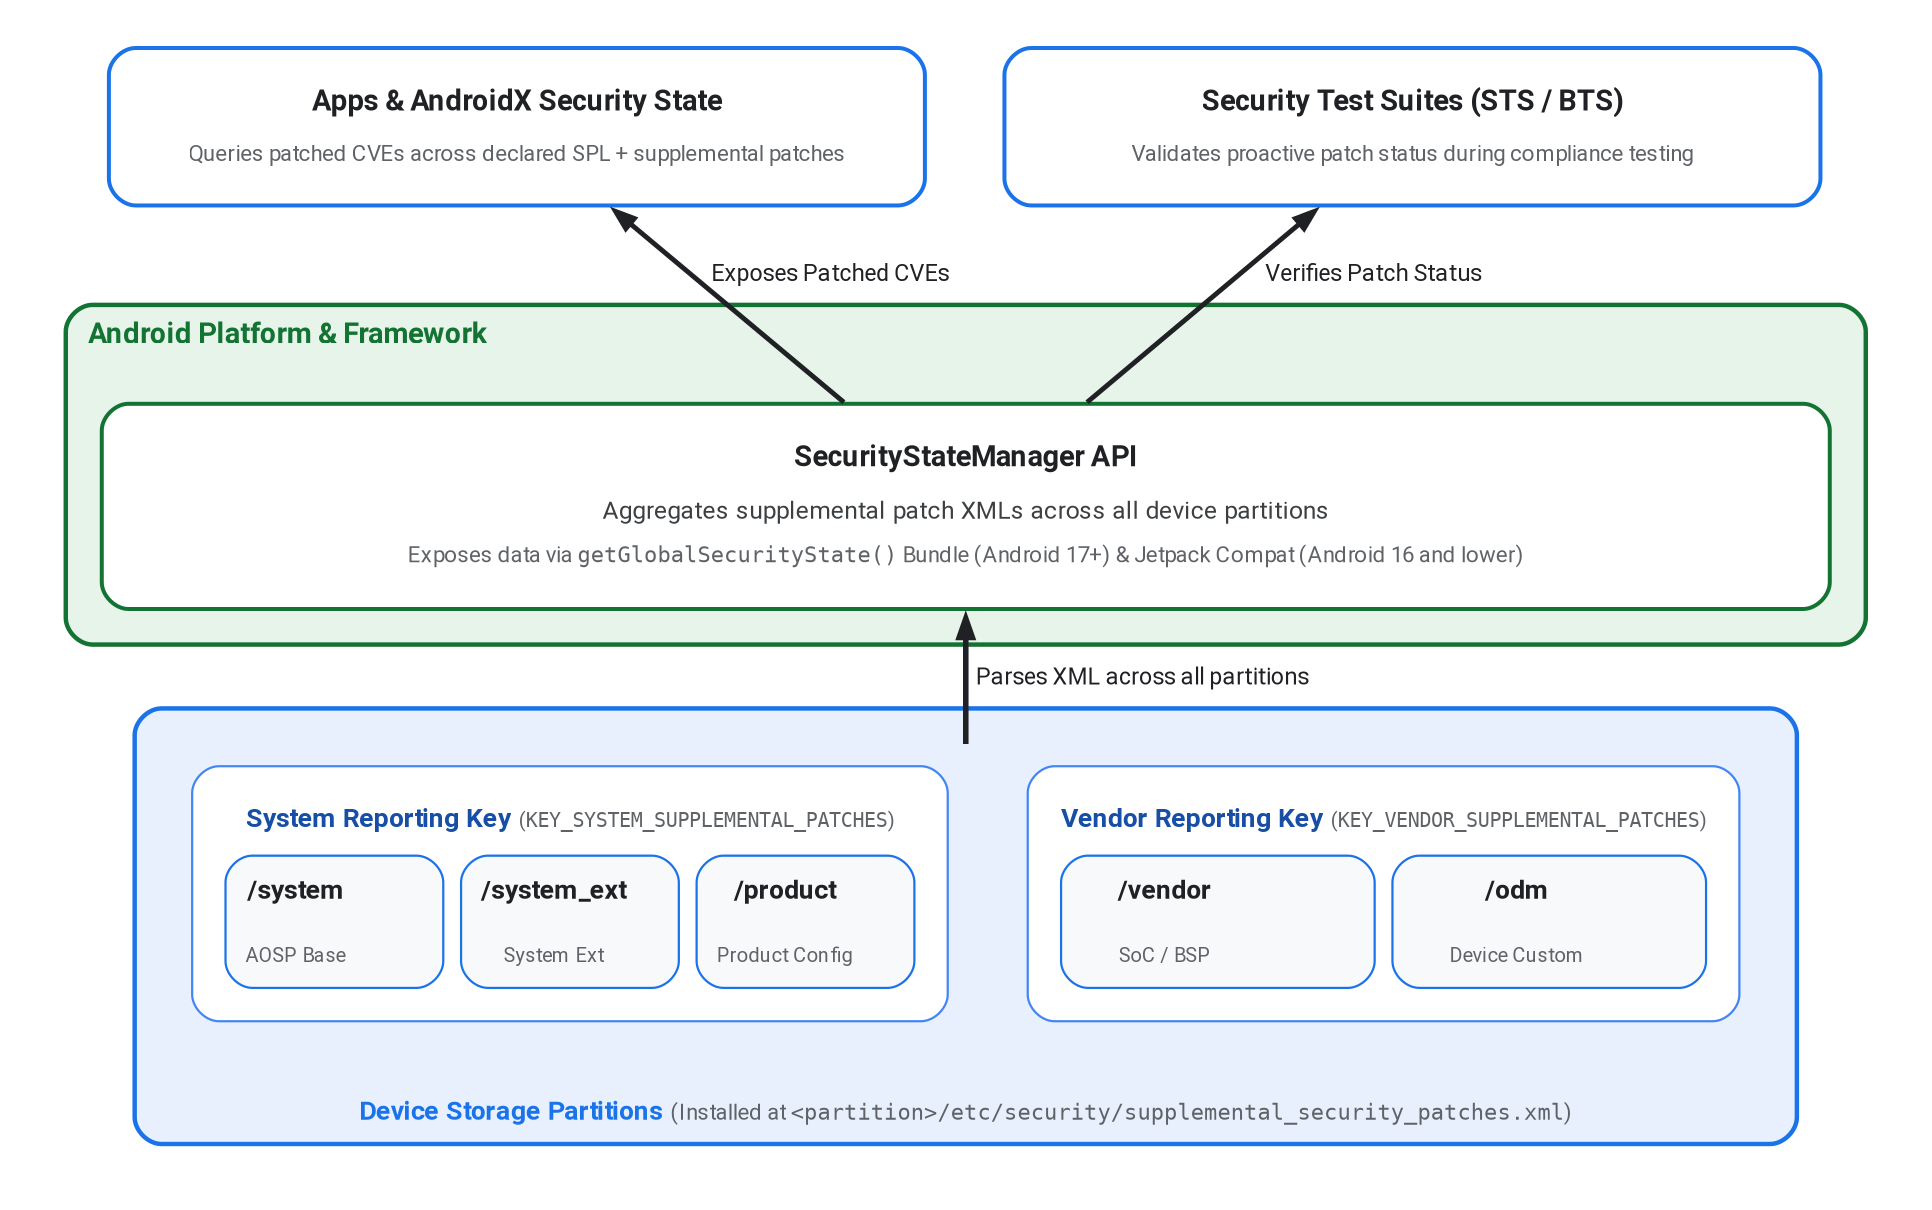
图 1. 补充安全补丁架构和数据传输。
OEM 可以将 XML 文件放置在多个设备分区(/system、/vendor 或 /product)中,确保框架和特定于硬件的组件中的安全补丁都得到考虑。XML 文件应安装在相应分区的 /etc/security/supplemental_security_patches.xml 中。
平台会汇总这些设备分区中的 CVE 数据,并在平台 API 和 Jetpack 库中公开这些数据。如需了解详情,请参阅平台 API Android 17 及更高版本和向较低 Android 版本进行反向移植。
以下示例展示了安装在 Android 设备上的补充安全补丁 XML 文件示例:
<?xml version="1.0" encoding="utf-8"?>
<security-patches xmlns="http://schemas.android.com/security/patches/1.0">
    <patch><id>CVE-2026-12345</id></patch>
</security-patches>
平台 API(Android 17 及更高版本)
对于 Android 17(API 级别 37)及更高版本,平台的 SecurityStateManager 会处理来自所有受支持分区位置的补充补丁,并使用键 KEY_SYSTEM_SUPPLEMENTAL_PATCHES 和 KEY_VENDOR_SUPPLEMENTAL_PATCHES 将它们公开在 getGlobalSecurityState 返回的 Bundle 中。
系统服务 SecurityStateManagerService 将分区 XML 文件汇总到以下两个总括报告桶中:
KEY_SYSTEM_SUPPLEMENTAL_PATCHES:汇总来自/system、/system_ext和/product分区路径的补丁。KEY_VENDOR_SUPPLEMENTAL_PATCHES:汇总来自/vendor和/odm分区路径的补丁。
向后移植到较低 Android 版本
对于 Android 16 及更低版本,没有平台 API 支持。相反,Jetpack androidx.security:security-state 库 (SecurityStateManagerCompat) 会使用 XmlPullParser 手动读取 XML 文件。为了允许 untrusted_app 网域在 Android 16 及更低版本上读取文件,OEM 必须在安装 XML 文件的所有分区路径中实现以下 SELinux 更改:
file_contexts:
/(system|vendor|product|system_ext|odm)/etc/security/supplemental_security_patches\.xml u:object_r:supplemental_security_patches:s0
supplemental_security_patches.te:
allow untrusted_app supplemental_security_patches:file { getattr open read };
构建规则和架构验证
如需将补充补丁 XML 文件安装到 /vendor/etc/security/、/system/etc/security/ 或 /product/etc/security/,请在 Android.bp 中添加 prebuilt_etc 规则。由于 SecurityStateManagerService 要求设备上的文件必须命名为 supplemental_security_patches.xml,因此在使用特定于分区的模块名称时,请使用 filename 属性:
// For vendor partition (/vendor/etc/security/supplemental_security_patches.xml)
prebuilt_etc {
    name: "vendor_supplemental_security_patches.xml",
    src: "supplemental_security_patches.xml",
    filename: "supplemental_security_patches.xml",
    sub_dir: "security",
    vendor: true,
}
// For system partition (/system/etc/security/supplemental_security_patches.xml)
prebuilt_etc {
    name: "system_supplemental_security_patches.xml",
    src: "supplemental_security_patches.xml",
    filename: "supplemental_security_patches.xml",
    sub_dir: "security",
}
// For product partition (/product/etc/security/supplemental_security_patches.xml)
prebuilt_etc {
    name: "product_supplemental_security_patches.xml",
    src: "supplemental_security_patches.xml",
    filename: "supplemental_security_patches.xml",
    sub_dir: "security",
    product_specific: true,
}
Android 开源项目 (AOSP) 在 supplemental_security_patches.xsd 中包含 XSD 架构,并在构建流程中使用 Android.bp 中的 xsdc 构建规则验证 XML 文件格式:
xsdc {
    name: "supplemental_security_patches_xsd",
    srcs: ["supplemental_security_patches/supplemental_security_patches.xsd"],
    package_name: "android.security.patches", // Java package name for generated code
}
您还可以使用 xmllint 在本地针对 XSD 架构验证 XML 文件:
xmllint --schema frameworks/base/services/core/xsd/supplemental_security_patches/supplemental_security_patches.xsd --noout supplemental_security_patches.xml
测试和套件集成
安全测试套件 (STS) 和 固件分析 (BTS) 使用 supplemental_security_patches.xml 文件中的数据来扩展对 XML 文件中存在的漏洞的补丁分析。因此,除了反映设备的安全性状态之外,正确集成此文件还可让 OEM 对设备 SPL 以上已修补的漏洞执行主动补丁分析,而无需等待季度 SPL 正式声明。